Product APIs
Offer consistent resources, validation, error contracts and authorization boundaries to client applications.
Clear APIs and platform boundaries help applications exchange information, evolve independently and work together over time.
For builders joining web and mobile experiences, external services, operational tools and reusable platform capabilities.
APIs should make it obvious what a system does, how it handles change and what happens when something fails. Well-chosen boundaries keep products adaptable without hiding complexity.
An API should be easy to understand, test and change without surprising its consumers. A platform should have obvious ownership and limits.
Offer consistent resources, validation, error contracts and authorization boundaries to client applications.
Connect billing, identity, messaging or business systems without coupling every product to every provider.
Share carefully chosen capabilities between experiences with clear internal contracts and observability.
These building blocks can be tailored to a concrete product need, team and technical environment.
Consistent resources, validation, versioning and predictable responses for developers and consumers.
Reusable identity, data and workflow services with explicit ownership and boundaries.
Connect external services with careful authentication, rate limits, timeouts and recovery paths.
Readable documentation, examples, test environments and integration diagnostics.
Consumers depend on published contracts; business services own policy; integrations adapt external systems.
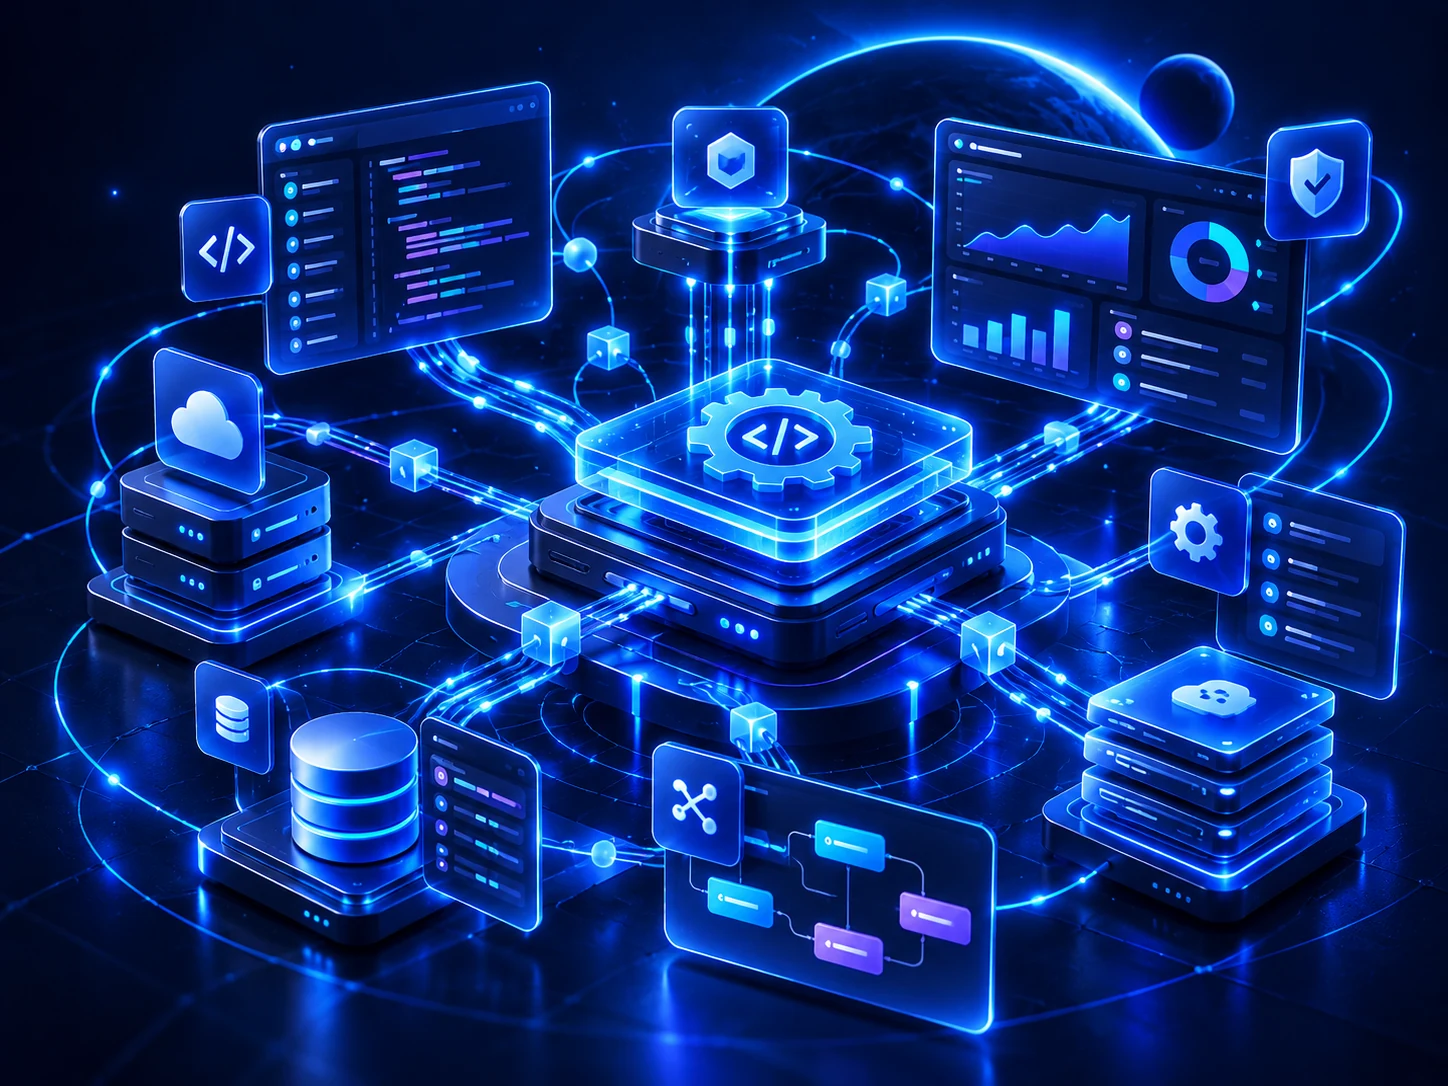 CONCEPT ILLUSTRATION · 05 / 05
Web apps · Mobile · Partner services
Authentication · Validation · Rate controls
Business rules · Data ownership · Events
Adapters · Queues · Metrics · Versioning
Service count should follow actual ownership and scaling needs; a modular monolith may be an excellent starting point.
A product has web and mobile experiences that need to share accounts, tasks and notifications without duplicating business logic.
Illustrative system journey — not an existing customer case study.Web and mobile products request capabilities through defined interfaces.
Authenticate and validate requests; enforce access rules.
Business rules coordinate data and third-party services.
Trace failures, version changes and maintain compatibility.
These are possible applications, not claims about past customer engagements. Every build starts with actual constraints and a defined outcome.
A mobile and browser product share a clear identity and permissions model without duplicating business logic.
External billing events update account state through validated, idempotent handlers with traceable exceptions.
Partners receive documented interfaces, predictable errors and a deliberate version-migration plan.
Start with what clients actually need to do.
Document schemas, errors, limits and compatibility expectations.
Use timeouts, idempotency and clear error semantics.
Scope and deliverables depend on the engagement. This is a representative process for planning and building the work responsibly.
Understand consumers, key entities and operations.
Define contracts, failures, security and change policy.
Implement tests, observability and useful examples.
Manage versions, deprecations and feedback responsibly.
Each deliverable is scoped and agreed before work starts.
Share the systems to connect, expected consumers, identity model, data sensitivity, rate constraints and compatibility needs.
Technology choices start with understanding the problem—not assuming a particular stack.
No. A modular monolith with well-designed APIs may be simpler and safer for a smaller product.
Prefer compatible evolution when possible, and introduce a clear versioning and migration plan for breaking changes.
Authenticate requests, authorize each operation, validate input, use appropriate transport protections and monitor abuse.
Share the idea, the constraints and the result you're aiming for. We'll explore a sensible direction together.